TL;DR: Server-side tracking can make permitted event delivery easier to control. It does not recover a fixed percentage of conversions, override consent or guarantee lower CPA. Start with an authoritative order source, shared event identifiers and a record of what each recipient receives.
A shop has 120 paid orders, Meta shows 146 purchases and GA4 shows 103. This is an illustrative example, not client data. Before increasing spend, explain the differences: delivery failures, duplicate events, payment definitions and attribution windows are different problems.
Our position is practical: server-side tracking connects a business event to a platform through a controlled transport. The useful outcome is a traceable order, not simply a higher dashboard score. Reducing CPA still requires checking the offer, creative and purchase journey.
Why browser tracking needs an independent reference
The Pixel remains useful for session context and permitted advertising identifiers. Its delivery depends on JavaScript, the browser, blockers, consent and the implementation. Apple’s App Tracking Transparency concerns tracking in apps; it is not a measured website consent rate. No common European loss percentage follows from adding overlapping browser, blocker and refusal estimates.
Safari blocks third-party cookies. WebKit also describes storage removal after seven days without interaction and limits for third-party CNAME/IP cloaking. A first-party-looking subdomain therefore does not guarantee a year of cookie persistence. Firefox separates cookies by website; Chrome maintains user choice for third-party cookies. These are distinct mechanisms. See WebKit, Firefox and Chrome’s published approach.
Measure your own coverage against the orders eligible for the relevant processing. Orders without advertising consent must not be treated as a technical backlog to send secretly through CAPI.
How the architecture works
Five components have different responsibilities:
- Website and browser tags: record permitted session actions and identifiers.
- Shop backend: confirms the order, payment, amount, currency, cancellation and refund.
- Stable event identity: links two deliveries of the same event to one business operation.
- Server container or endpoint: validates inputs, applies recipient-specific rules, removes unnecessary fields and routes the event.
- Restricted logs and reconciliation: show acceptance, rejection, retries and delivery failures without retaining unnecessary customer data.
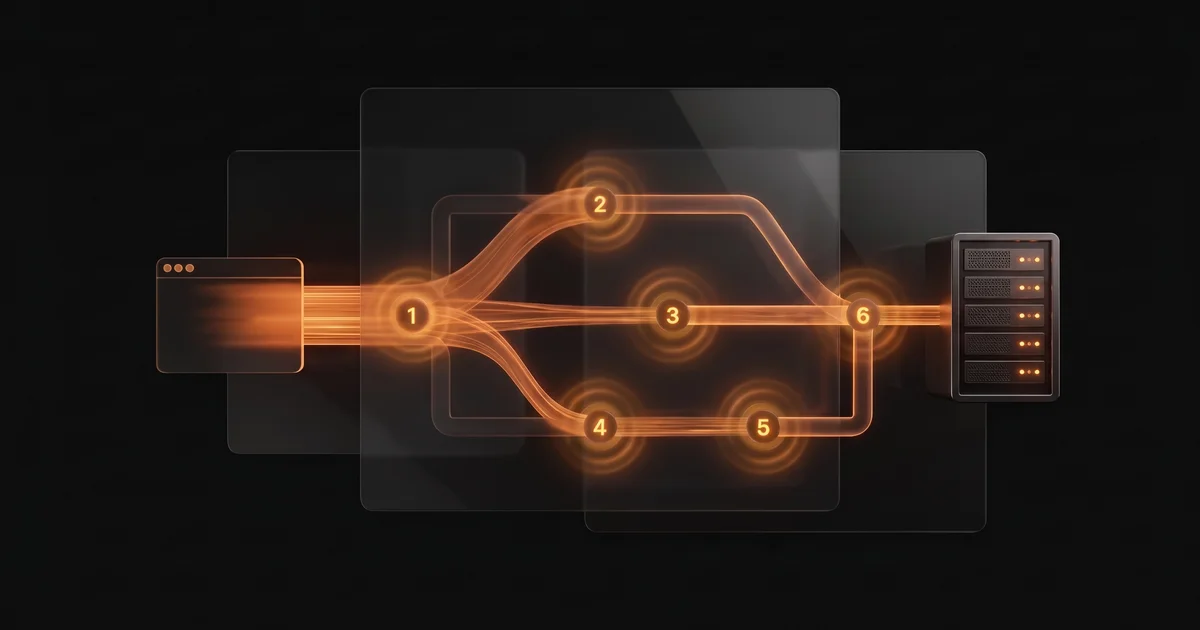
The browser route is action → consent rules → browser request → endpoint. An independent backend route is confirmed operation → permitted server event → endpoint. Both then pass the recipient’s rules before forwarding. A browser dataLayer push is not a backend webhook; an endpoint fed only by a blocked browser request cannot recreate a missing order by itself.
Google server-side Tag Manager supports Cloud Run and other compatible infrastructure. A direct CAPI endpoint is another option. GA4 Measurement Protocol is an API for sending Analytics events, not another name for sGTM. Choose infrastructure by support capacity, volume, access controls and cost. A subdomain such as tracking.example.test helps manage the route; it does not make tracking invisible to blockers or lawful automatically.
Client-side and server-side comparison
| Question | Practical distinction |
|---|---|
| Collection | Browser action and backend payment are different sources |
| Blockers | Independent backend delivery avoids a browser request; browser-fed routes retain that dependency |
| Cookies | Lifetime depends on browser policy and implementation, not a universal server-side duration |
| Consent | Apply the choice before browser collection and each relevant server destination |
| EMQ | Inspect matching inputs; neither route has a guaranteed score |
| Deduplication | Pair browser and server deliveries using the same event name and ID |
| Matching | Use permitted fields and their individual normalization rules |
| Documentation | Record purposes, recipients, access, retention and transfers in either architecture |
| Cost | Compare implementation, hosting, subscription and maintenance together |
| Time | Depends on checkout, event sources, consent and acceptance requirements |
Meta CAPI: matching, identity and data quality
Event Match Quality is a diagnostic of customer information used for matching. It does not prove the amount is correct, duplicates are absent, processing is lawful or an attributed sale is incremental. There is no universal score below which Meta “guesses” or above which ROAS must rise. Meta’s public CAPI training description treats redundancy, deduplication, freshness and matching as separate areas.
Deduplication requires consistent event_name and event_id for two deliveries of one event. Generate the identifier once in the system that knows the order; reuse it on retry and when the thank-you page reloads. Give different operations distinct IDs. Meta deduplication and GA4 transaction handling need separate checks; GA4 DebugView does not prove Meta’s result. See the deduplication guide.
An offline example of a shared identifier
The following JavaScript defines synthetic objects; it sends no request and includes no token. The timestamp is a fixed teaching value, and the hash represents a synthetic address. It is not a payload to copy into a live account.
const eventId = "purchase_demo_123";
const pixelExample = {
  eventName: "Purchase",
  parameters: { currency: "EUR", value: 149.90, content_ids: ["demo-product"] },
  options: { eventID: eventId }
};
const serverPayload = {
  data: [{
    event_name: "Purchase",
    event_time: 1767225600,
    event_id: eventId,
    event_source_url: "https://shop.example.test/order-confirmed/",
    action_source: "website",
    user_data: { em: ["63eb9cd45e0f3a8f895141aeac8810840bc12ae3d939b752766b7ea52bff76f9"] },
    custom_data: { currency: "EUR", value: 149.90,
      content_ids: ["demo-product"], content_type: "product" }
  }]
};
The Pixel option is eventID; the server field is event_id. Meta’s official SDK event model describes the ID together with the name. Production validation must also inspect actual delivery and platform processing; matching two objects locally does not establish either.
Advanced Matching may use email, phone, names, city or postcode where necessary and permitted. Normalize each field by its own specification before hashing where required. IP address, user agent, fbp and fbc are not all subject to the same SHA-256 recipe. Never invent click/browser identifiers or collect extra demographic fields solely to raise EMQ. The SDK user-data model distinguishes these fields. Hashing does not turn personal data into anonymous data.
Keep Meta matching data separate from ordinary GA4 event parameters, URLs and logs. Google Analytics prohibits sending recognizable PII, including email and personal phone numbers.
Consent and the Austrian legal context
Google’s four states include ad_storage, analytics_storage, ad_user_data and ad_personalization. The web CMP communicates choices to the Google tag, which carries consent parameters to the server container. Google tags then adjust behavior. Server-side Consent Mode supports basic and advanced implementations: basic blocks relevant Google tags until consent; advanced can send measurements without the relevant cookies after refusal. That technical behavior is not legal clearance for a particular deployment or permission for Meta CAPI.
Set defaults before relevant tags run, apply updates and withdrawal, and check each destination separately. Evaluate modeling separately from event delivery; a modeling estimate does not confirm receipt of a particular order.
DSB Austria distinguishes technically necessary cookies from those requiring prior consent. Advertising funding does not itself make cookies necessary. A server consent check does not repair a misleading banner or establish every GDPR requirement. Review purposes, legal basis, processors, retention and international transfers; EU hosting alone is insufficient.
The Data Act is not evidence that every shop must deploy server-side advertising tracking. The Commission’s explanation concerns data access and sharing, including connected products. Claimed DSB priorities or fines require specific decisions, not a link to the authority’s homepage.
What the internal cases show
In our ongoing engagement with Czech online retailer Erkado, work combines server-side event tracking, segmented campaigns across three distinct goals (e-commerce sales, B2B leads, and showroom hiring), and mobile checkout UX adjustments guided by Clarity observations. This demonstrates that reliable tracking infrastructure establishes data clarity, but works in concert with campaign management rather than driving isolated revenue leaps alone.
In our Fashion demonstration framework, structured alignment between creative messaging, on-page sizing guidance, and transparent checkout terms is modeled end-to-end. This highlights that trust elements and cohesive ad angles work in concert, rather than acting as isolated performance guarantees.
Implementation: five phases and seven checks
The five phases are audit → infrastructure → integration → validation → monitoring. Agree scope and acceptance before estimating price or duration. A fixed fee or four-week payback cannot follow from the shop’s ad budget alone.
Seven checks make those phases concrete:
- Event map: source, trigger, fields, recipients and rules for PageView, ViewContent, AddToCart, InitiateCheckout and Purchase.
- Business reference: distinguish order placement, payment, cancellation and refund; the thank-you page is not the sole payment evidence.
- Infrastructure: DNS, TLS, capacity, roles, server-only tokens, retention and restricted logs.
- Identity: browser/server pairing, reload, retry, collision, partial-payment and refund scenarios.
- Matching: permitted fields, individual formats and separate Analytics routing.
- Consent: initial state, grant, refusal, partial choice and withdrawal at each recipient.
- Reconciliation: compare a known operation through isolated fixtures, GTM Preview, authorized platform diagnostics and backend records before release. Assign an owner, alert criteria and rollback plan.
Do not send fabricated purchases to a live account to make a dashboard green. Monitoring follows changes to the CMP, checkout and platform integration; neither a universal EMQ target nor 48 hours alone proves readiness.
Frequently Asked Questions
How does server-side tracking differ from the Pixel?
The Pixel observes permitted browser actions. A server route processes events in controlled infrastructure and can receive an independent backend fact. They complement one another; neither overrides consent.
What does implementation cost?
Inventory the platform, events, checkout, CMP, hosting, access and monitoring. Compare setup and recurring support together. There is no universal price or payback period for all shops.
Do I still need the Pixel with CAPI?
A hybrid can preserve permitted browser context and an independent server source. Use shared names and identifiers to pair deliveries. The right design depends on the store and permitted processing.
What does EMQ establish?
It helps diagnose matching inputs. It does not establish order value, correct deduplication, attribution accuracy, legal compliance or profit, and does not guarantee lower CPM.
How long does implementation take?
Estimate after reviewing the checkout, sources, consent and access. Completion means validated identity, recipient rules and order reconciliation, with support in place, rather than merely installing a container.
If your shop and advertising reports disagree, describe the difference in an initial discussion. Tracking & CAPI covers diagnostics and implementation agreed separately by scope.