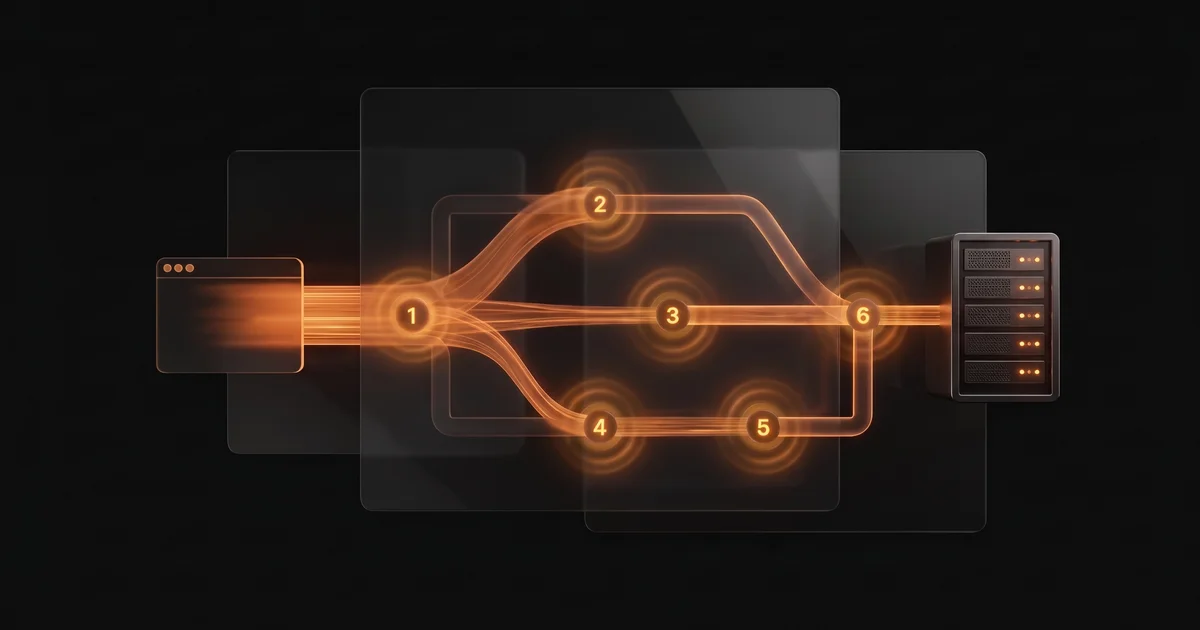
TL;DR: Meta Conversions API adds a server route to browser event transmission. A reliable setup needs a clear purchase definition, stable event IDs, appropriate data fields and rules for the user’s consent decision. Server-side GTM is one possible architecture. A higher Event Match Quality score alone establishes neither complete measurement nor cheaper sales.
A purchase exists in the shop but is missing from the ad report. Or one order is sent repeatedly through two integrations. Before adding CAPI, define the source, meaning and repetitions of the event. Otherwise an additional transmission route can amplify an existing error.
Choose the appropriate integration
First check which partner integration or direct server connection the shop already uses. GTM can be useful when it provides needed control over event routes, tags and ownership. It is not mandatory above a particular ad budget. The server-side tracking guide explains the architecture; common tracking errors help with the inventory.
In our ongoing engagement with Czech online retailer Erkado, work combines server-side event tracking, segmented campaigns across three distinct goals (e-commerce sales, B2B leads, and showroom hiring), and mobile checkout UX adjustments guided by Clarity observations. This demonstrates that reliable tracking infrastructure establishes data clarity, but works in concert with campaign management rather than driving isolated revenue leaps alone.
What to establish before configuring CAPI
Meta access and ownership
- The Business Portfolio and dataset or Pixel receiving the events;
- Events Manager access and permissions required for the selected integration;
- An access token kept exclusively in the protected server environment;
- An owner for permissions, token rotation and delivery errors.
Do not request every administrative permission or API scope by default. The required permissions and token type depend on the integration. Revocation, account changes or validity conditions can interrupt a token; document how the owner restores the connection.
Server infrastructure
- A GTM Server Container or another controlled endpoint;
- Suitable operations with error logs and restricted access;
- A first-party subdomain where it belongs to the selected architecture;
- Ownership of the cloud project, budget and maintenance.
Google explains clients, events and tags in its official introduction to server-side tagging. The hosting region, providers and agreements must fit the actual processing. An address in Frankfurt or another EU data centre does not establish GDPR compliance by itself.
Event source in the shop or backend
- A stable order
transaction_id; - One confirmed point for creating the
event_id; - Value, currency, items and payment status from a controlled source;
- Rules for failed payments, cancellation, refunds and repeated page loads.
Consent and permitted fields
- A CMP or another traceable choice process;
- Documented data categories and processing purposes;
- Transmission of the user’s choice to the server route;
- Separate checks for Google and Meta.
Google Consent Mode controls supported Google tags using consent signals. It does not provide a general permission for third-party tags. Meta needs its own rules for the actual processing. Google: server-side Consent Mode.
Step 1: Create one event source and event_id
For a purchase, the backend can create an event ID once after confirmed payment and store it with the order. Browser and server routes receive the same value. Reloading the confirmation page or repeating a payment webhook must not create a new purchase with a new ID.
A simplified example without customer information:
// orderData contains backend-confirmed, non-personal purchase fields.
window.dataLayer = window.dataLayer || [];
window.dataLayer.push({
  event: 'purchase',
  event_id: orderData.purchaseEventId,
  ecommerce: {
    transaction_id: orderData.id,
    value: orderData.total,
    currency: orderData.currency,
    items: orderData.items.map((item) => ({
      item_id: item.sku,
      item_name: item.name,
      price: item.price,
      quantity: item.quantity,
    })),
  },
});
orderData is an explanatory object, not a complete shop integration. The backend must already have generated and persisted purchaseEventId. It must be unique for each independent purchase and identical on both routes. Protect against collisions across shops too. Tag firing also respects the valid user choice; a dataLayer entry does not itself authorise transmission.
Three rules:
- Create
event_idonce. Do not useDate.now()on each render or generate a fresh UUID on every delivery attempt. transaction_ididentifies the order. It must not contain the customer’s email, phone number or name. Event IDs and order numbers serve different purposes.- Keep customer fields in the appropriate protected route. Necessary and permitted Customer Information Parameters do not need additional copies in public page code, consoles or general analytics logs.
For other events, a UUID stored with the originating action can work. A repeated delivery of that action keeps the ID; a new action receives a different one.
Step 2: Connect the server container and Meta tag
Create the container and tagging server in the controlled environment. Configure the route and client that understand the selected request format. Google’s data transmission guide provides background; its official setup documentation describes server_container_url for the Google tag. This Google setting does not replace an appropriate Meta tag or its consent rules.
For the CAPI tag, check the dataset or Pixel, protected token, event name, event_id, occurrence time and correct action_source. For a website purchase the source is website. Explicitly map a GA4 purchase event to Meta Purchase; arbitrary automatic reuse of the name is insufficient.
Inspect the template’s origin, version, permissions and normalization. A community template does not become an official Meta tag because of its name. A test code belongs to controlled validation, not permanently to ordinary delivery.
Confirmed order + stored purchaseEventId
  -> browser Pixel, when permitted: Purchase + eventID
  -> protected server route, when permitted: Purchase + event_id -> Meta CAPI

Permitted analytics event -> server client -> GA4 tag -> GA4
Permitted customer matching fields -> Meta-specific server route only
Do not forward Meta matching emails or phone numbers to GA4. Even a shared server container needs separate recipient rules and filters. Google states that prohibited personal identifiers do not belong in ordinary Analytics data, URLs or parameters. Google Analytics: avoid PII.
Inspect each tag’s outgoing request, not only the incoming request. Some tags can carry additional fields forward; transformations or explicit field lists must limit the disclosure.
Step 3: Deduplicate browser and server events
For the same action, both routes must send the same Meta event name and ID to the same dataset. The browser uses the Pixel option eventID; the server uses event_id. Similar aggregate browser and server counts do not establish this relationship.
The official Meta SDK Event class describes how event_name and event_id identify matching browser and server events. Meta’s public CAPI training also identifies deduplication, freshness and matching as areas to check.
Inspect specific pairs: source order, name, ID, dataset, occurrence time and confirmed processing. Remove unintended additional sources such as a second shop integration. A server count twice as large is a reason to investigate, not a diagnosis by itself.
| Teaching example with €1,000 in ad spend | Calculation and meaning |
|---|---|
| 50 actual purchases, only 40 captured | €1,000 / 40 = €25 recorded CPA. Investigate why events are missing. |
| 50 actual purchases counted as 100 across two routes | €1,000 / 100 = €10 apparent CPA. This assumed scenario contains complete duplicate copies. |
| 50 actual purchases each counted once | €1,000 / 50 = €20 measured CPA. This does not establish contribution margin or advertising incrementality. |
The numbers illustrate arithmetic, not a general loss rate. Compare the same purchase definition and period. Consent, technical capture and advertising attribution can produce different populations.
Step 4: Select matching fields deliberately
Event Match Quality describes matching quality, not the proportion of all orders or profitability. A target score such as 7 or 8 does not replace acceptance checks. More available fields are not an instruction to collect unnecessary customer information.
| Field group | What to check |
|---|---|
Email em | Permitted source; required normalization and hashing according to the field specification before Meta delivery. |
Phone ph | Country code and digit format required by Meta; do not automatically hash an E.164 string including +. |
Names fn / ln | Actual necessity and permission; appropriate normalization and processing. |
Location ct / st / zp / country | Suitable existing information and rules for each field; no extra collection solely to improve a score. |
Birth date / gender db / ge | Not default collection recommendations; assess necessity and permitted use separately. |
Internal identifier external_id | Purpose, stability and required preparation; do not expose an email as a public ID. |
Browser and click identifiers fbp / fbc | Source, validity and permission; do not apply email normalization or hashing indiscriminately. |
| IP / user-agent | Actual source and permitted disclosure; no invented values or universal SHA-256 procedure for every field. |
The official Meta SDK UserData class treats normalized customer fields differently from IP, user-agent, fbp and fbc; it describes phone values as digits including country and area codes. Also check the current API specification and actual template. Hashing does not automatically make personal-data processing anonymous or permitted.
Step 5: Validate the whole chain before release
Start with controlled test data and clearly separated test routes. Testing in a real shop can create real orders or advertising events and needs its own approved procedure.
Four validation layers:
- Test Events: inspect names, sources, fields and IDs; a success message is not evidence of revenue.
- GTM Preview: trace the incoming request, responsible client, triggers and outgoing tags.
- Diagnostics: investigate errors, missing fields and additional sources rather than waiting only for a better score.
- Business reconciliation: compare confirmed orders, amounts and states with the source system over the same period.
Check consent in four states: before a choice, after refusal, after permission and after withdrawal. Inspect both browser and server routes each time. Blocking the Pixel while continuing server transmission is insufficient.
Six failure scenarios:
- Reloading the confirmation page;
- Repeating a payment webhook;
- Failed or unconfirmed payment;
- Cancellation and refund according to documented rules;
- Switching language, domain or shop environment;
- Changed or withdrawn user permission.
Eight technical acceptance checks
- The source action and its owner are clear.
- Both routes receive the same stable ID for the same action.
Purchaseactually represents a confirmed purchase.- Value, currency and items match the shop records.
- The user’s choice affects every relevant route.
- Retries and additional integrations do not create unintended duplicate purchases.
- Tokens and unnecessary customer details are absent from public code and GA4.
- Monitoring, error handling and changes have an owner.
Problems that can appear after launch
Shop or CMS changes: a new checkout can change triggers or field paths. Recheck the purchase flow after relevant releases.
Tokens and permissions: revocation, validity conditions or access changes can interrupt delivery. Errors and ownership must be visible.
Consent changes: a CMP update can change categories or signals. Repeat the four user-choice scenarios.
A second event source: an additional partner integration may transmit alongside GTM. Check routes and IDs together.
Incorrect purchase meaning: a form, initiated payment or updated order is not automatically another paid purchase. The business definition remains authoritative.
A higher EMQ after a fixed number of hours, or a lower CPM after a week, does not establish a correct implementation. Monitor delivery failures, event relationships and deviations from permitted source events over an appropriate period.
What a sound implementation can provide
It creates an owned event process, adds a second permitted transmission route, allows relevant business stages to be represented deliberately and makes errors easier to diagnose. It guarantees neither a fixed recovery percentage nor a CPA reduction. Further reading: tracking errors and assessing CPA through the business process.
Frequently Asked Questions
Does CAPI replace the Meta Pixel?
Not universally. Both routes can complement each other where permitted and where they transmit the same action with consistent names and IDs. The appropriate combination depends on the actual integration.
Does every shop need its own GTM Server Container?
No. First assess the existing partner integration or direct server connection. Another container makes sense when its control and maintenance meet a concrete need without creating an uncontrolled second event source.
Must every Customer Information Parameter be transmitted?
No. Use necessary and permitted fields from a suitable source. A matching score does not justify collecting sensitive or unnecessary information. Normalization and hashing depend on the individual field and current specification.
How do you establish that the setup works?
Through traceable source events, stable IDs, correct amounts, tested user choices and effective deduplication. Compare processing with the business system. EMQ and successful API responses alone are insufficient.
Does EU hosting automatically make the setup GDPR compliant?
No. Region, agreements, purposes, fields, access and onward transfers need to be assessed together. An EU server does not replace those checks.
Want to clarify the existing event route? Discuss the setup with Canem Errant →